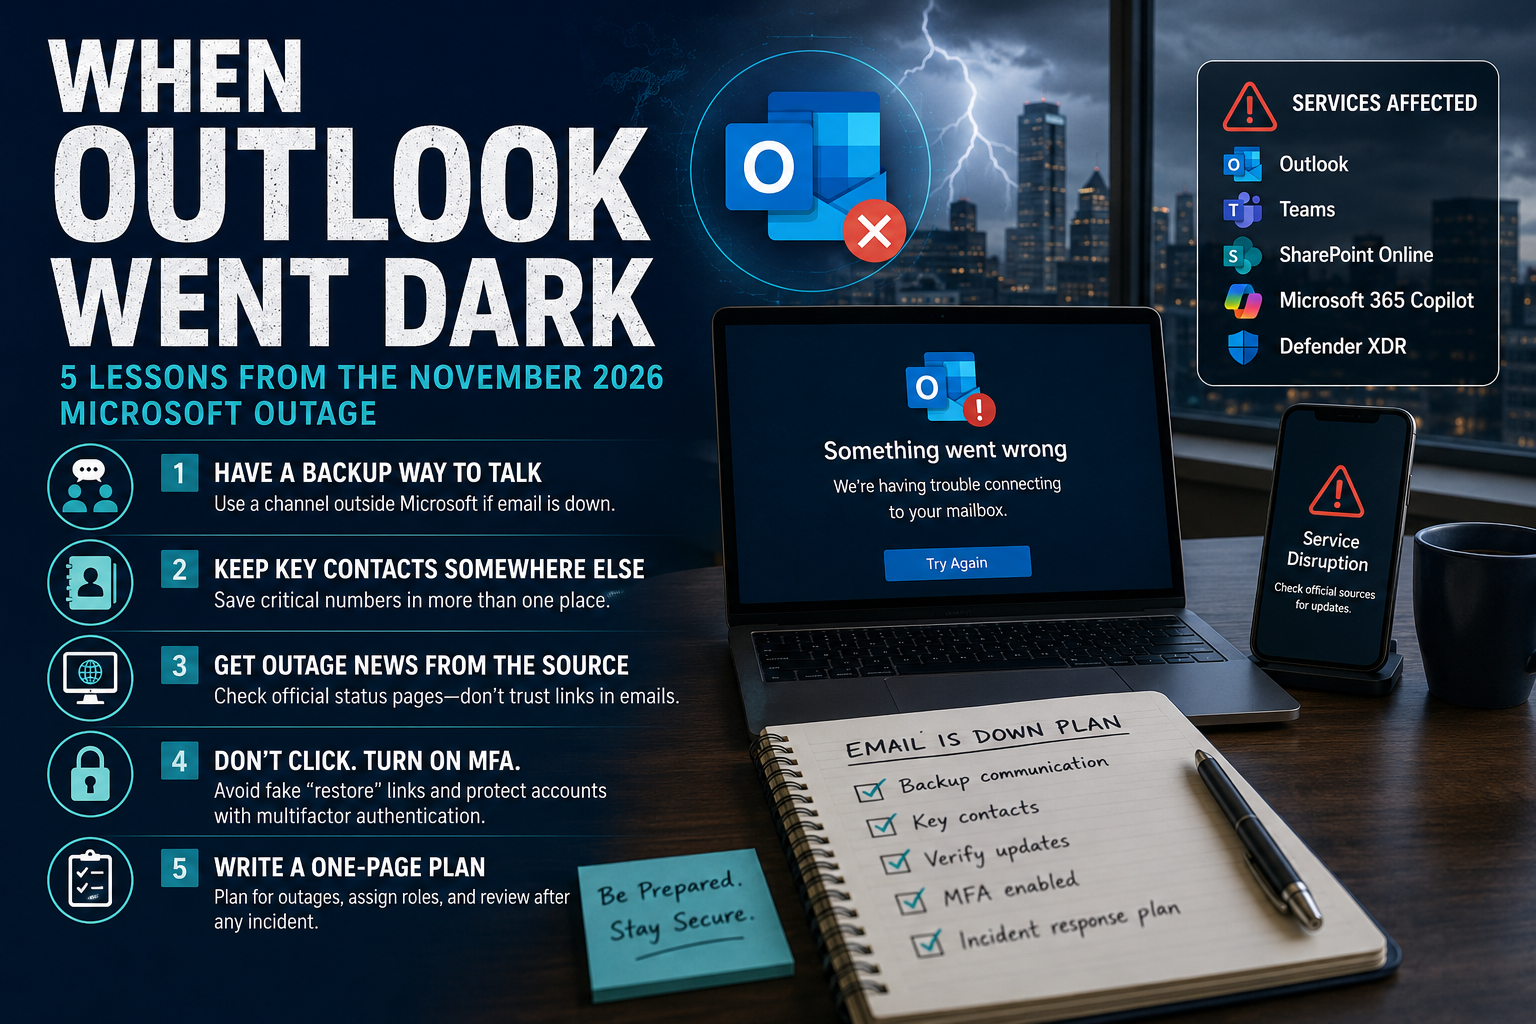
When Outlook Went Dark: 5 Lessons From the November 2026 Microsoft Outage

When Outlook Went Dark: 5 Lessons From the November 2026 Microsoft Outage

What happened

At lunchtime on Thursday, November 12, millions of people opened Outlook and got nothing. No new mail, no calendar, no way to send.

Microsoft first reported trouble reaching Exchange Online mailboxes in the Americas just before noon Eastern. Outage reports on Downdetector peaked at roughly 130,000 in the U.S. (Newsweek). It wasn't only email: Teams, SharePoint Online, Microsoft 365 Copilot and Defender XDR were also affected (ABC10).

The disruption ran into Friday. Microsoft apologized and said it was not a cyberattack and not related to AI agents (ABC7 New York). Even after service came back, a backlog of delayed email was still working its way through.

No hack, no data stolen. So why is a cybersecurity blog writing about it? Because outages test the same thing attacks do: whether your business can keep running when a system you depend on suddenly isn't there.
Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

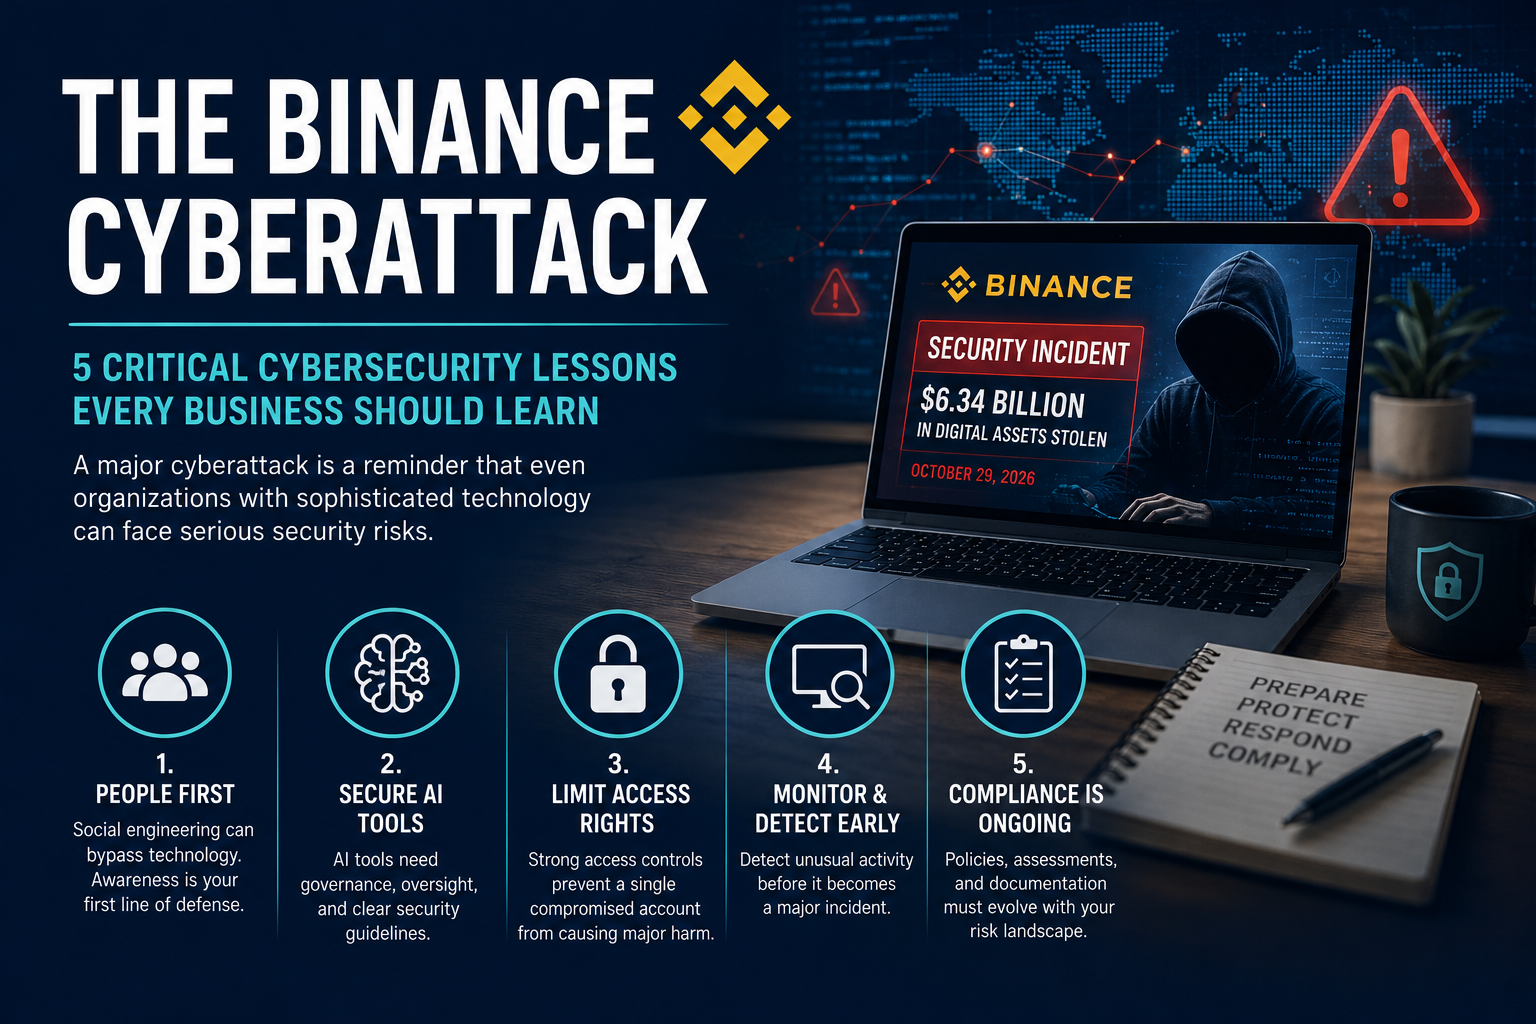
The Binance Cyberattack: 5 Critical Cybersecurity Lessons Every Business Should Learn

The Binance Cyberattack: 5 Critical Cybersecurity Lessons Every Business Should Learn

A major cyberattack is a reminder that even organizations with sophisticated technology can face serious security risks.

On October 29, 2026, cryptocurrency exchange Binance experienced a significant security incident involving approximately $6.34 billion in digital assets across multiple blockchain networks. The FBI attributed the theft to North Korea and identified the activity as TraderTraitor. Binance's initial investigation revealed a sophisticated, multi-stage attack involving compromised employee devices, social engineering, malicious software, internal AI tooling, and unauthorized access to wallet-signing operations.

While the incident involved cryptocurrency infrastructure, its lessons extend far beyond the financial and digital asset industries.

For businesses managing sensitive information, customer data, government contracts, or regulated operations, the Binance incident raises an important question:

Are your cybersecurity controls designed to prevent a single compromised employee, device, or application from putting your entire organization at risk?

At Ultimate Risk Services (URS), we believe cybersecurity is not just about having security tools. It is about identifying risks, implementing appropriate controls, maintaining compliance, and ensuring organizations can demonstrate that their security practices are working.

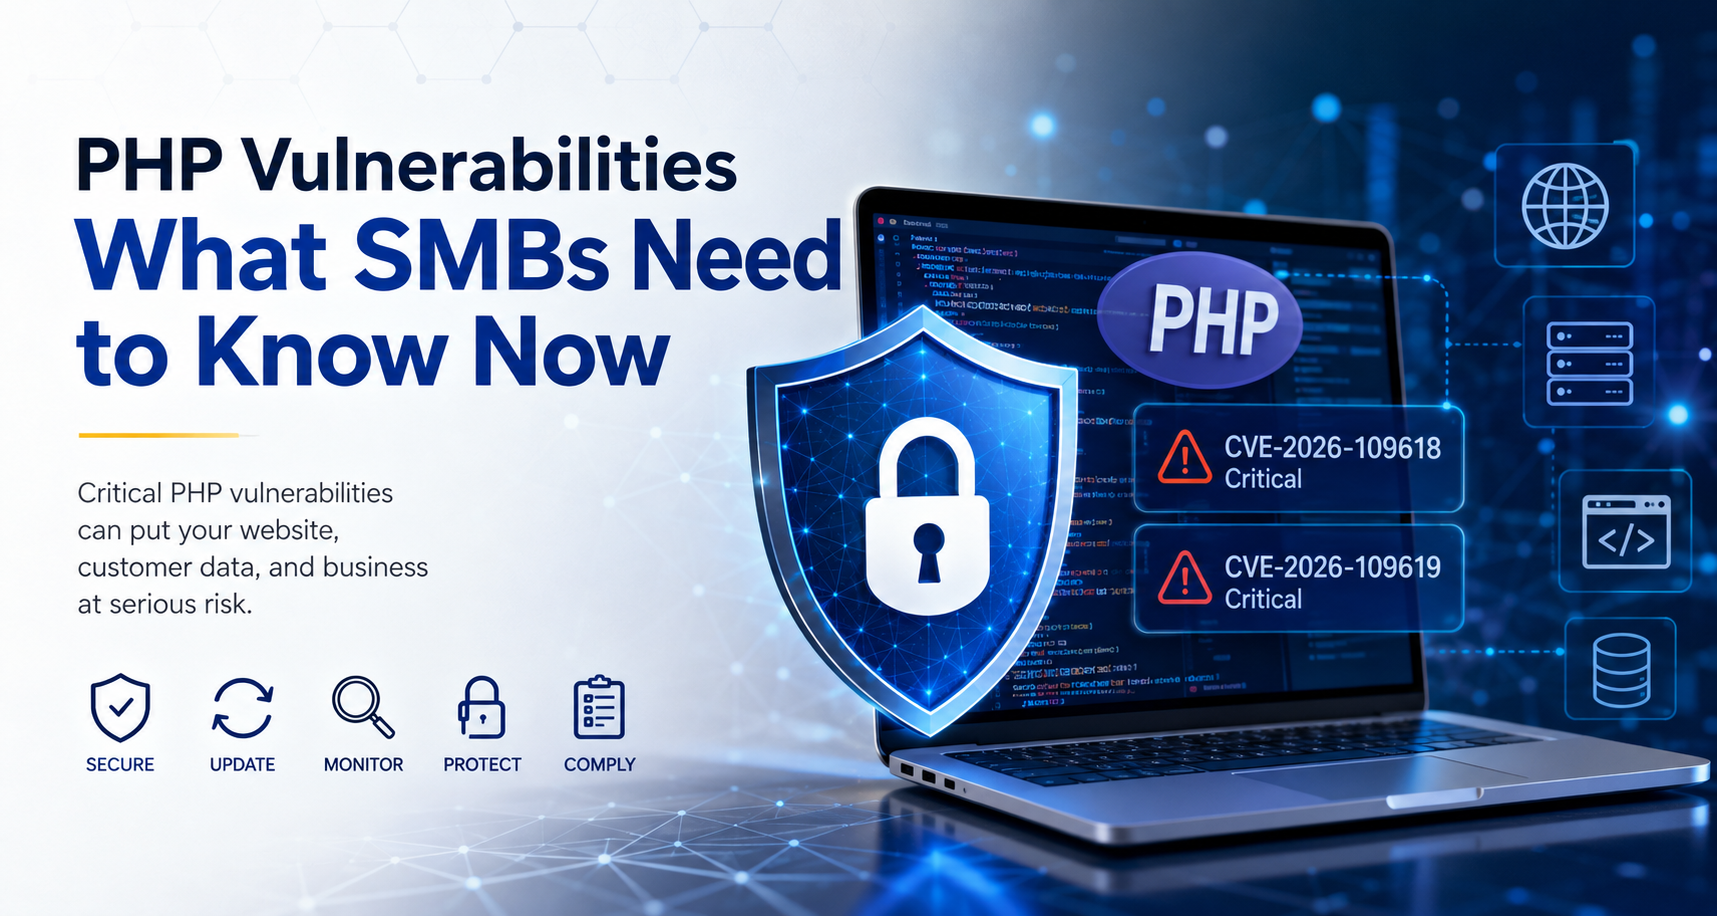
PHP Vulnerabilities: How SMBs Can Protect Their Websites, Data, and Stay Compliant

PHP Vulnerabilities: How SMBs Can Protect Their Websites, Data, and Stay Compliant

Protecting your website is more than keeping your software running. It is about protecting your business, customer information, and compliance responsibilities.

PHP is one of the most widely used programming languages for websites and web applications. It powers platforms, business portals, e-commerce websites, and content management systems that organizations rely on every day.

However, vulnerabilities in PHP can create significant cybersecurity risksโ€”especially for SMBs that depend on third-party website developers, hosting providers, or managed IT service providers (MSPs).

In October 2026, two critical PHP vulnerabilities, identified as CVE-2026-109618 and CVE-2026-109619, brought renewed attention to the importance of timely security updates. These vulnerabilities could allow attackers to execute malicious code on affected servers without authentication.

For SMBs, the message is clear: keeping your website, applications, and underlying technology updated is a business security responsibilityโ€”not just an IT task.

Cybersecurity Awareness Month: How to Turn Cybersecurity Awareness Into a Stronger, More Resilient Business

Cybersecurity Awareness Month: How to Turn Cybersecurity Awareness Into a Stronger, More Resilient Business

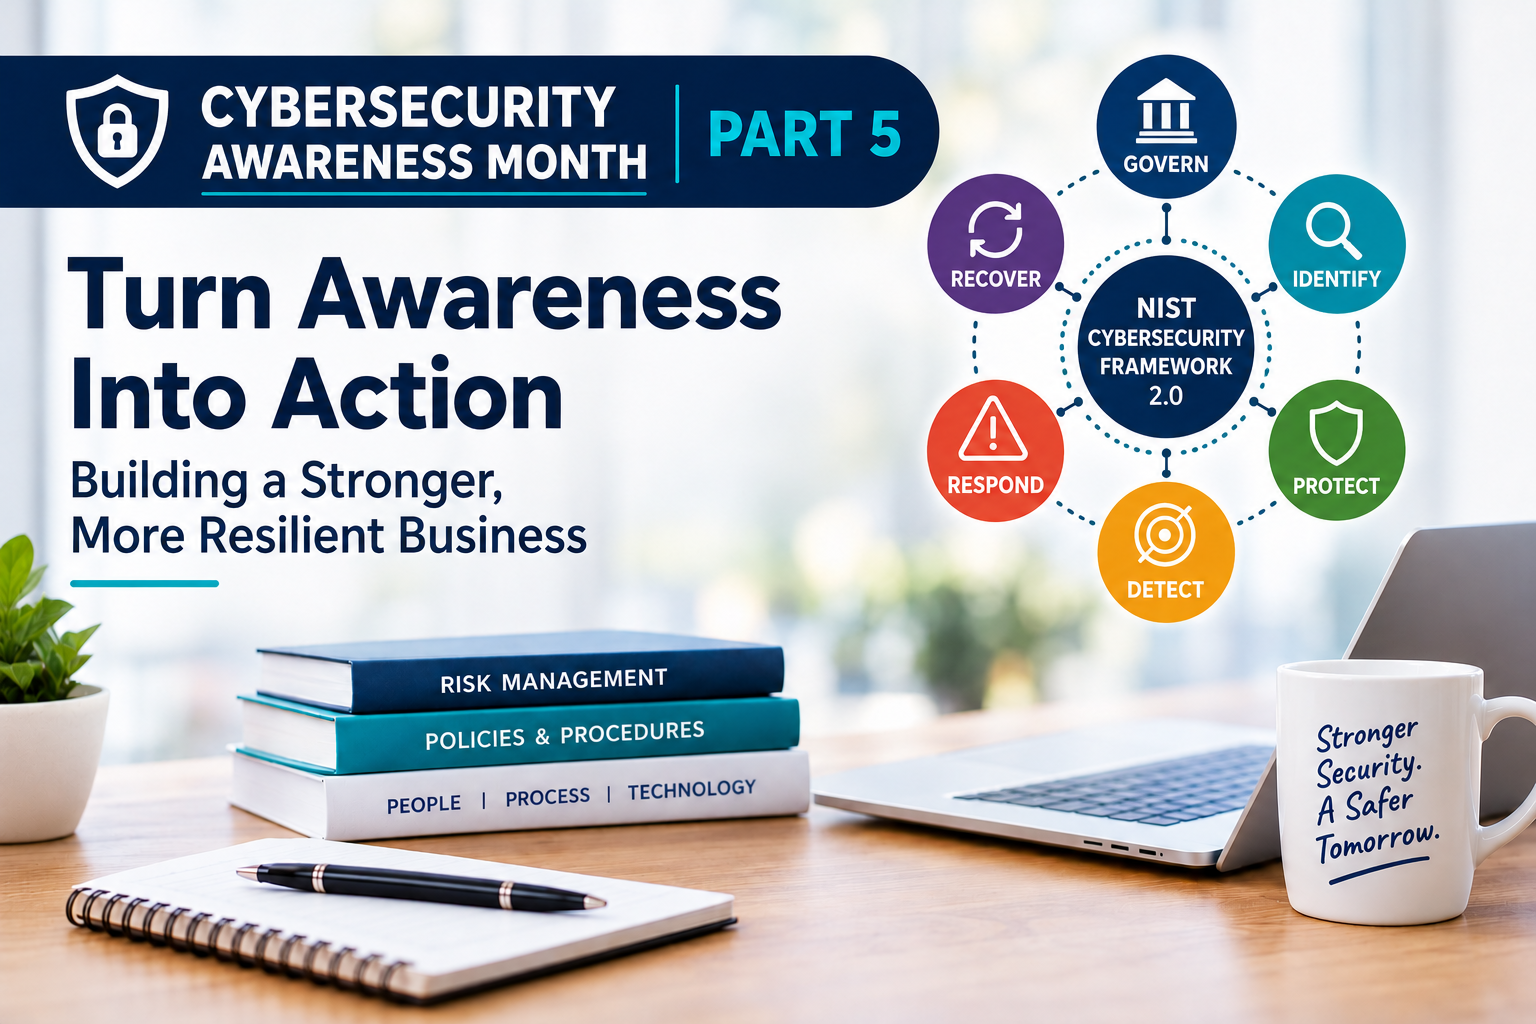
URS Cybersecurity Awareness Month: Part 5

Awareness Is Only the Beginning

Throughout Cybersecurity Awareness Month, we have explored the importance of protecting digital identities, recognizing phishing, managing cybersecurity risks, and understanding compliance requirements.

But awareness alone is not enough.

Businesses must turn cybersecurity knowledge into practical action.

That means identifying risks, implementing safeguards, preparing for incidents, and continuously improving security practices.

Cybersecurity is not a one-time project.

It is an ongoing process that helps organizations protect their information, maintain operations, and build customer trust.

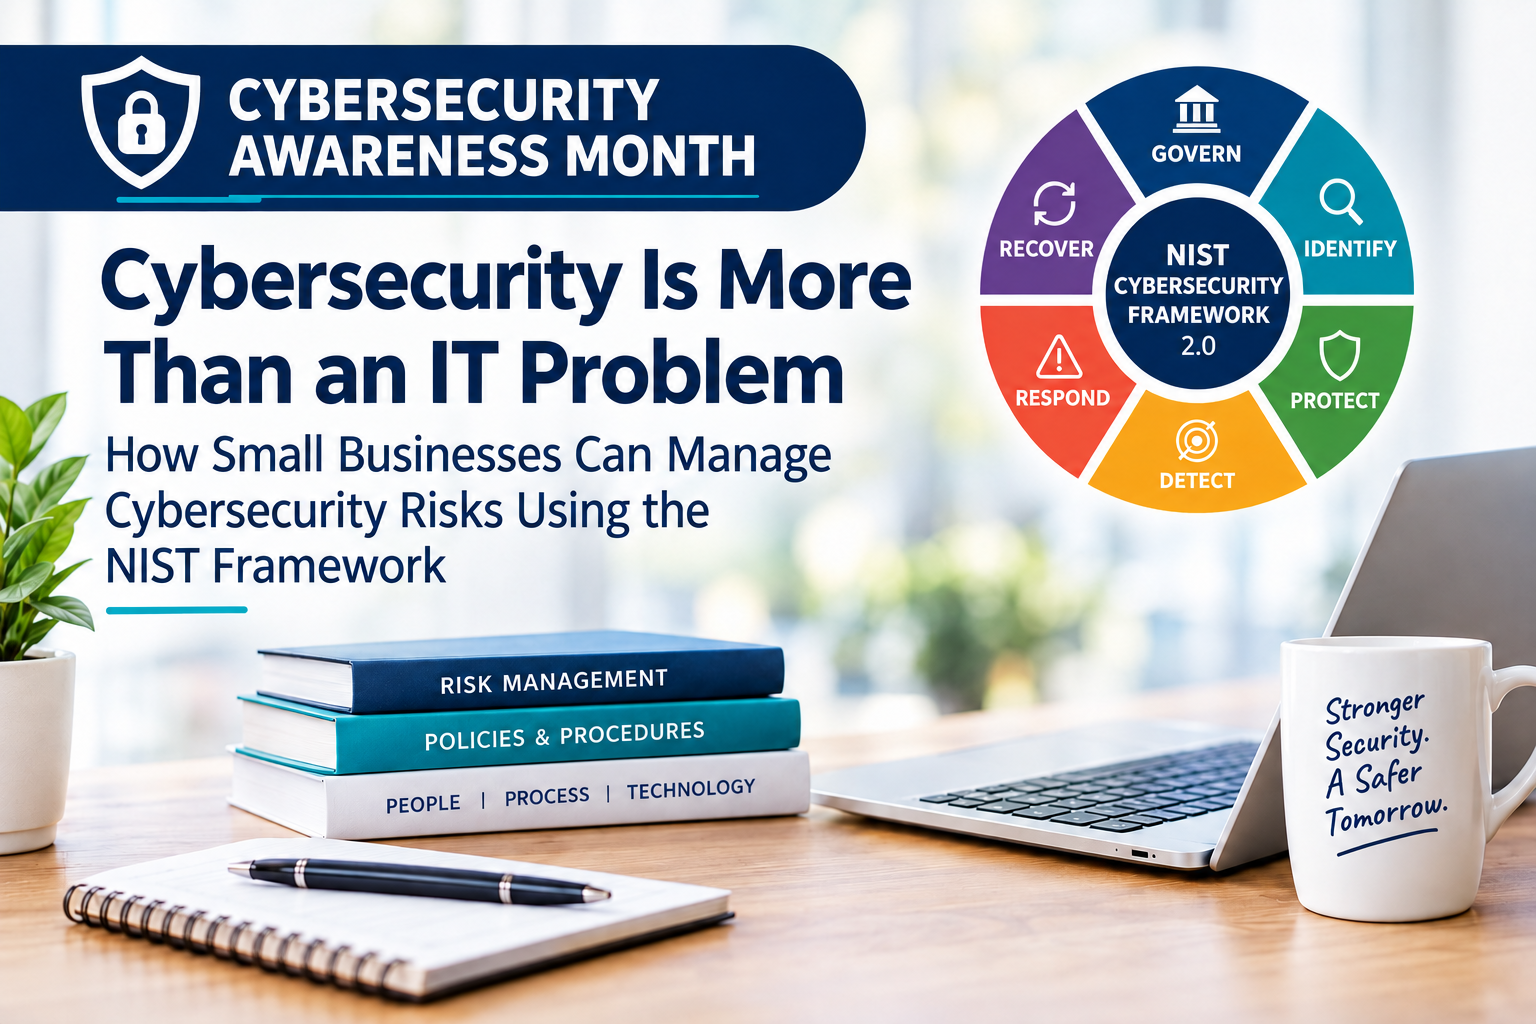
NIST's Cybersecurity Framework 2.0 provides a structured approach to managing cybersecurity risks through its six functions: Govern, Identify, Protect, Detect, Respond, and Recover.

Cybersecurity Awareness Month Part 4 : What HIPAA, PCI DSS, and CMMC Mean for Your Business

Cybersecurity Awareness Month Part 4 : What HIPAA, PCI DSS, and CMMC Mean for Your Business

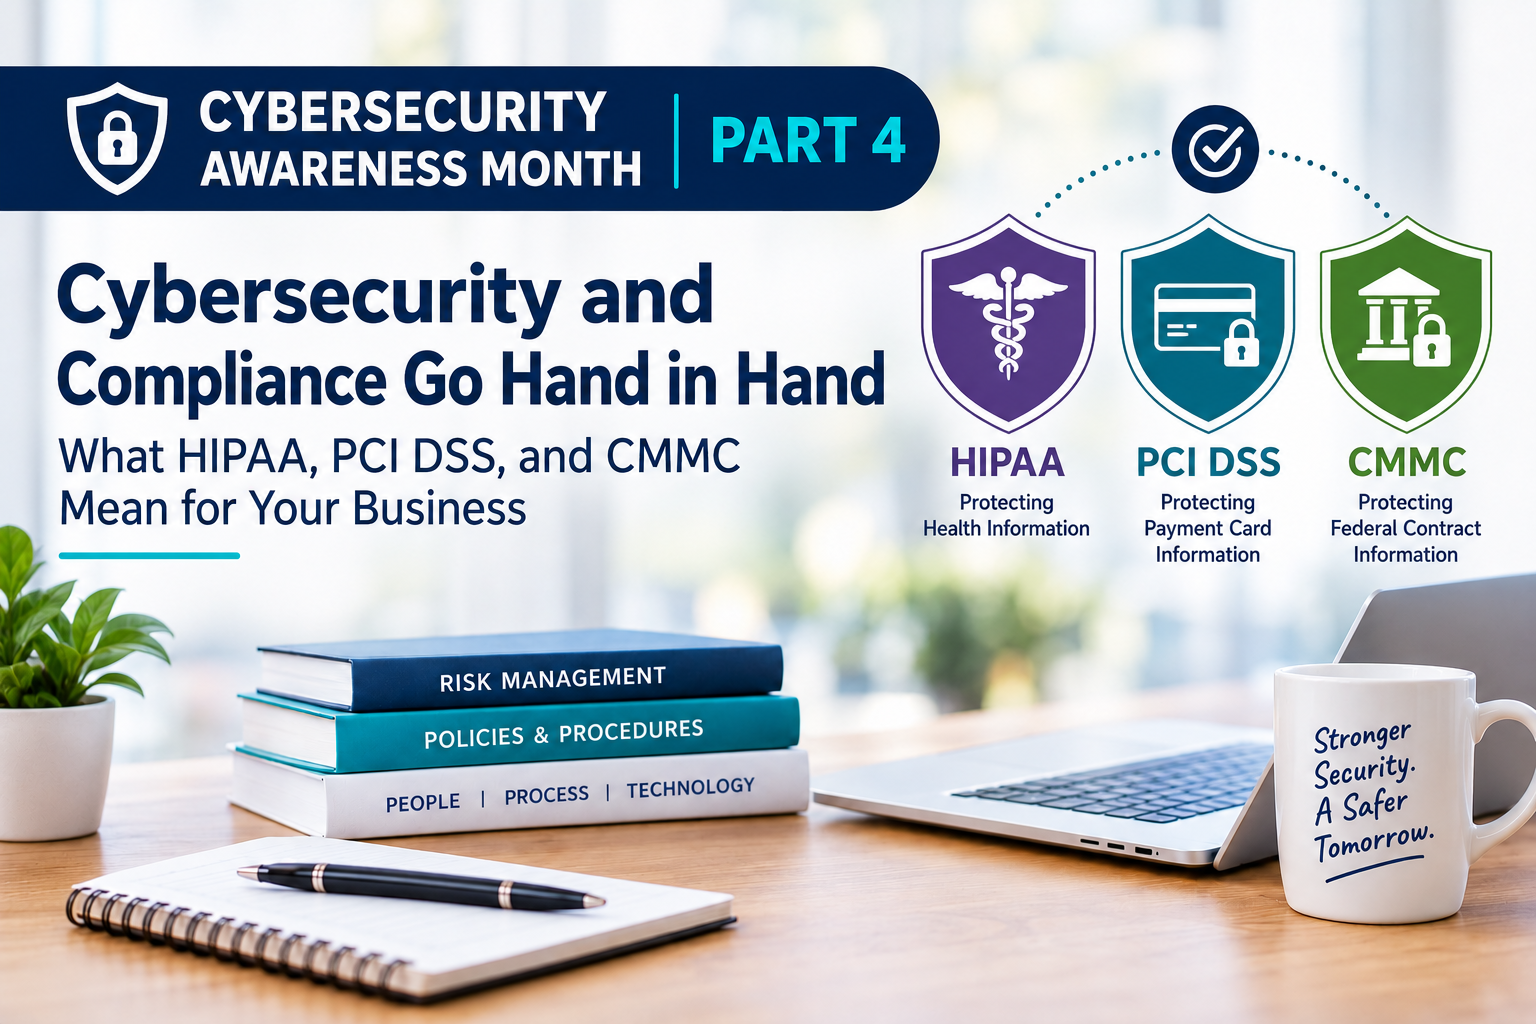
URS Cybersecurity Awareness Month: Part 4

Introduction: Cybersecurity and Compliance Go Hand in Hand

Cybersecurity is not only about protecting systems from hackers.

For many organizations, it is also about meeting regulatory, contractual, and industry-specific requirements.

Businesses may be required to demonstrate that they have implemented appropriate safeguards to protect sensitive information.

These requirements can vary depending on the organization's industry, the type of information it handles, and the contracts it holds.

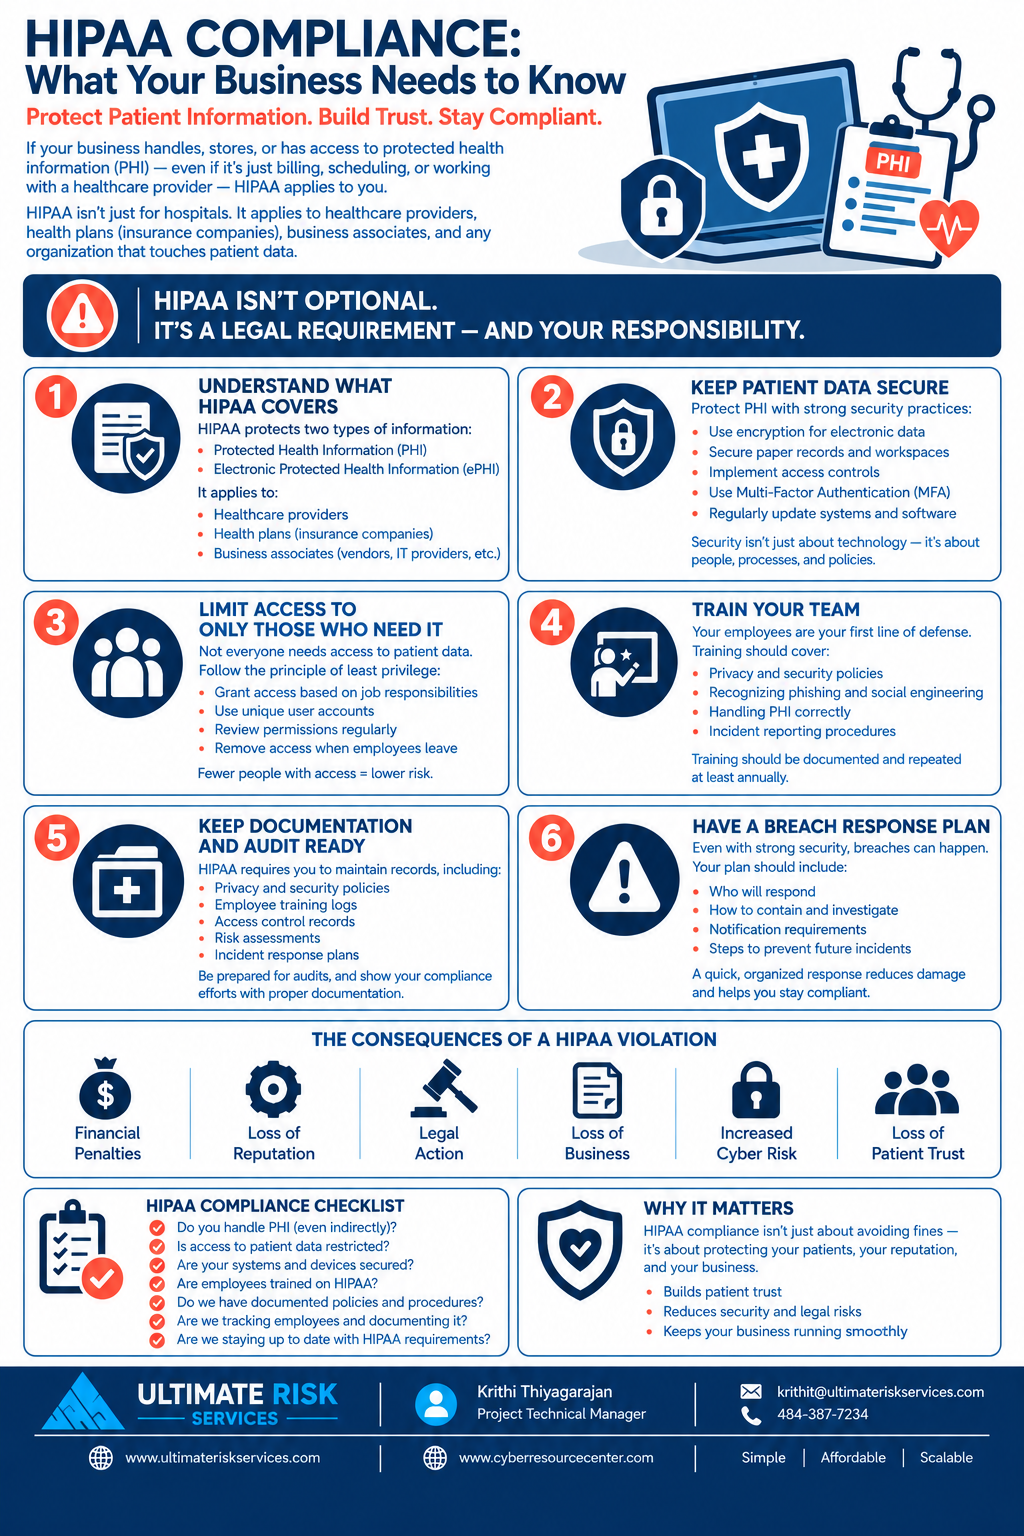
Healthcare organizations may be subject to HIPAA.

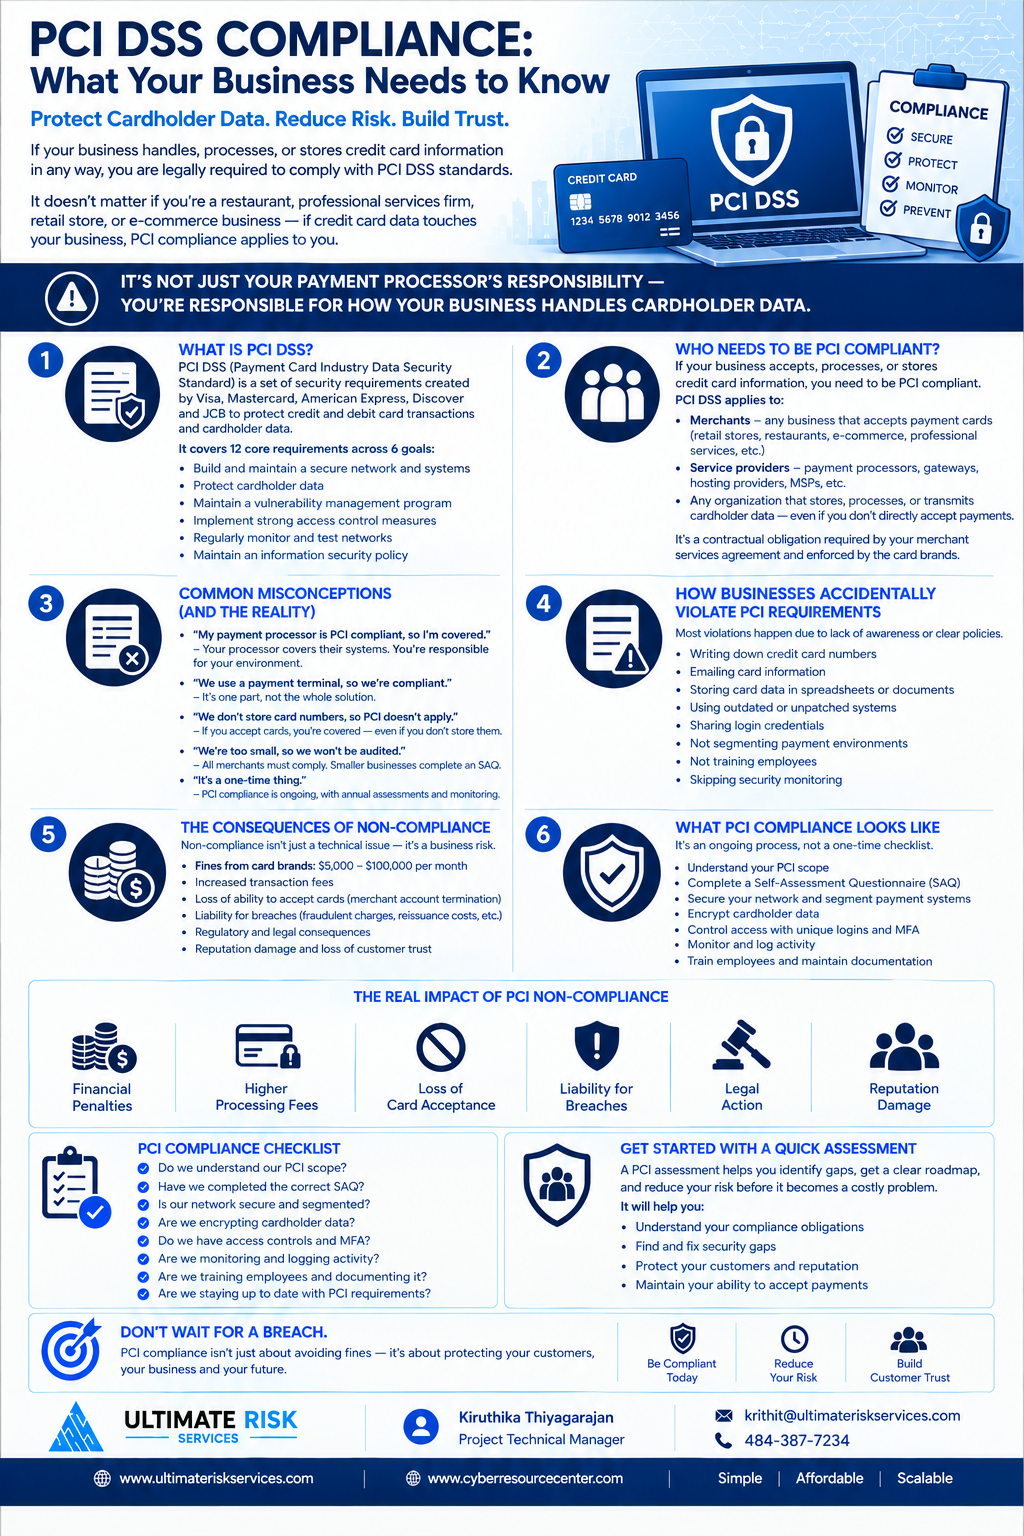
Businesses that handle payment card information may have PCI DSS responsibilities.

Federal contractors handling certain government information may be subject to CMMC requirements.

Understanding which requirements apply is an important step toward developing an effective cybersecurity and compliance program.

Cybersecurity Awareness Month: How Small Businesses Can Manage Cybersecurity Risks Using the NIST Framework

Cybersecurity Awareness Month: How Small Businesses Can Manage Cybersecurity Risks Using the NIST Framework

URS Cybersecurity Awareness Month: Part 3

Introduction: Cybersecurity Is More Than an IT Problem

Many business owners think cybersecurity is simply about installing antivirus software, purchasing a firewall, or hiring an IT provider.

While these measures are important, cybersecurity involves much more than technology.

It is a business risk that can affect operations, finances, customer trust, regulatory compliance, and long-term growth.

A business may have excellent technology but still face cybersecurity risks because of inadequate policies, excessive user access, outdated procedures, or a lack of employee awareness.

The National Institute of Standards and Technology (NIST) developed the Cybersecurity Framework (CSF) to help organizations understand, assess, prioritize, and manage cybersecurity risks.

NIST CSF 2.0 is organized around six core functions: Govern, Identify, Protect, Detect, Respond, and Recover.

Cybersecurity Awareness Month Part 2: How to Protect Your Digital Identity From Phishing, Account Takeovers, and Cyber Scams

Cybersecurity Awareness Month Part 2: How to Protect Your Digital Identity From Phishing, Account Takeovers, and Cyber Scams

URS Cybersecurity Awareness Month: Part 1

Introduction: Your Digital Identity Is Valuable

Every day, we use digital accounts to communicate, work, shop, manage finances, and access sensitive information.

Our email accounts, social media profiles, banking applications, and business systems contain information that cybercriminals may attempt to steal or misuse.

A compromised account can create consequences that extend far beyond a single login.

For individuals, it may lead to financial fraud, identity theft, or loss of personal information.

For businesses, a compromised employee account can provide attackers with access to confidential information, customer records, financial systems, or other business resources.

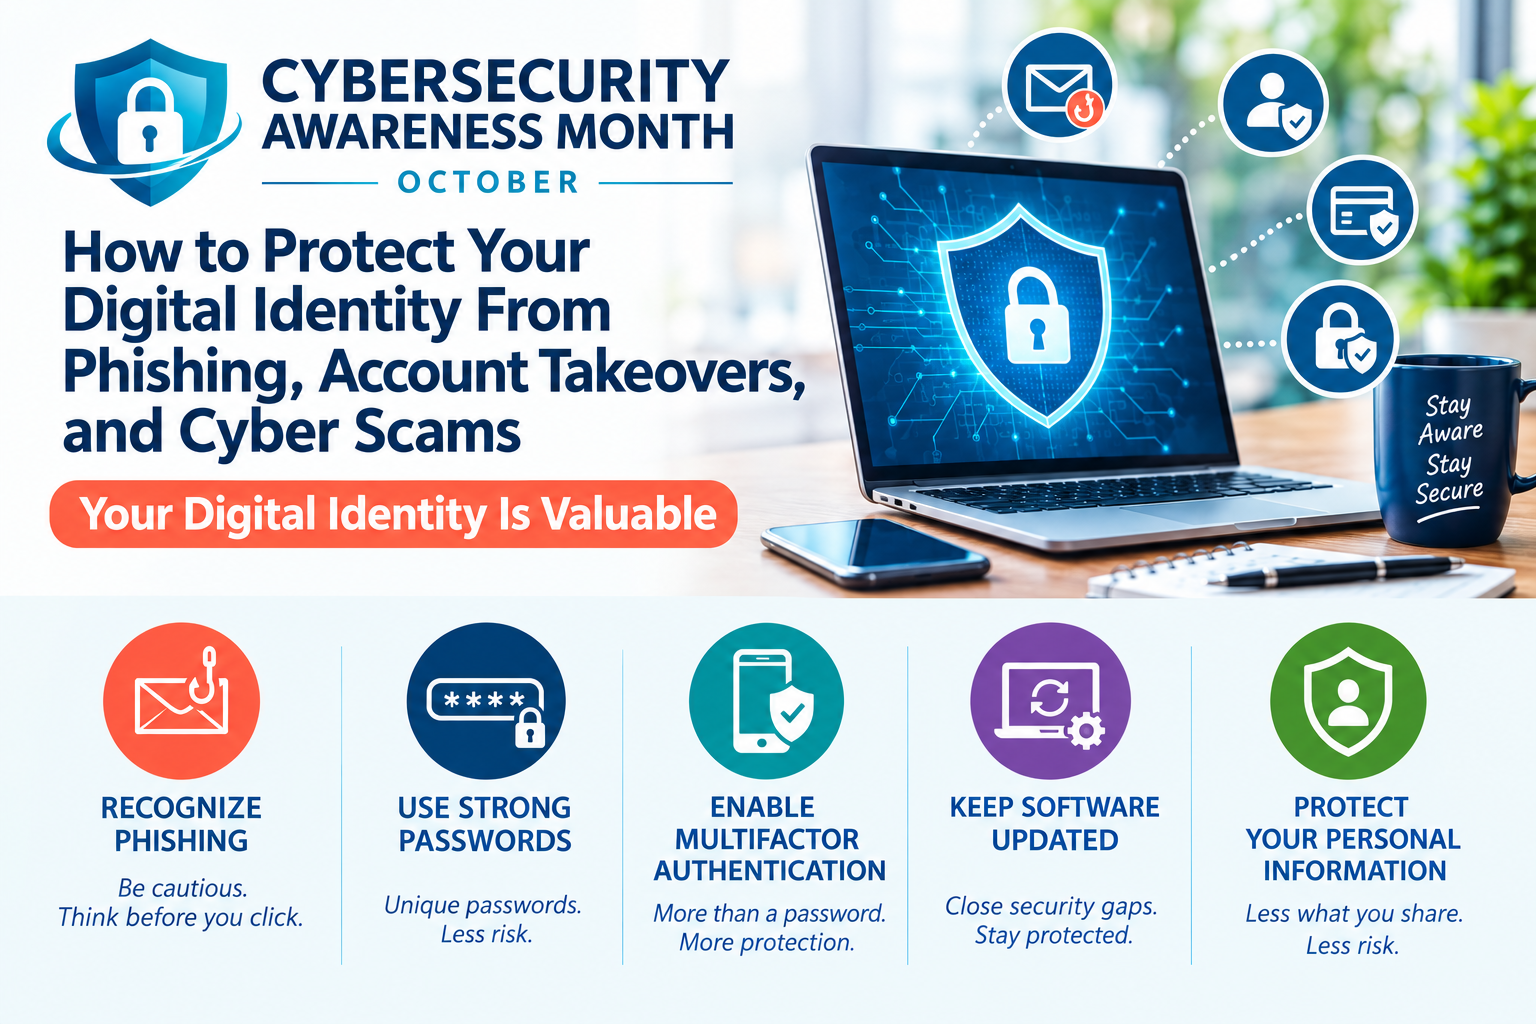
The Cybersecurity and Infrastructure Security Agency (CISA) recommends four foundational cybersecurity practices: recognizing and reporting phishing, using strong passwords, enabling multifactor authentication, and updating software.

Cybersecurity Awareness Month Part 1: 5 Essential Steps Every Business Should Take to Stay Cybersecure

Cybersecurity Awareness Month Part 1: 5 Essential Steps Every Business Should Take to Stay Cybersecure

URS Cybersecurity Awareness Month: Part 1

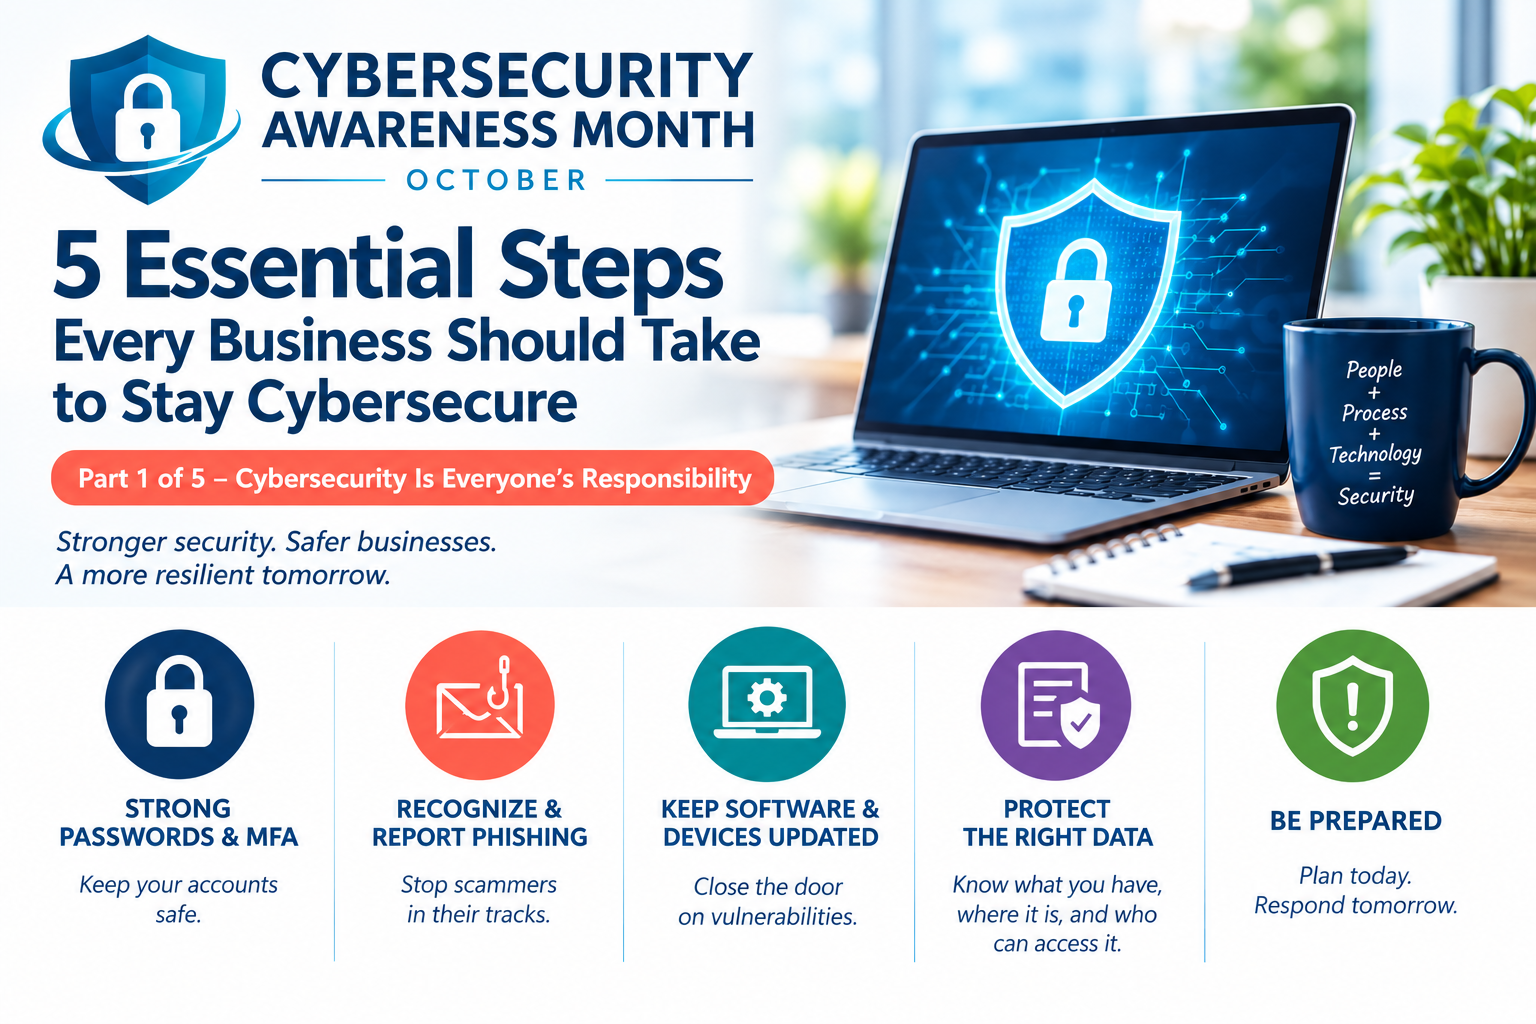
Cybersecurity Is Everyone's Responsibility

October is Cybersecurity Awareness Monthโ€”a reminder that protecting digital information is a shared responsibility.

In 2026, CISA's Cybersecurity Awareness Month campaign, "Securing the Next 250," emphasizes the importance of strengthening cybersecurity and protecting the systems and services that businesses and communities depend on.

But cybersecurity is not just a concern for large corporations or government agencies.

Small businesses, healthcare providers, manufacturers, financial organizations, and individuals all rely on technology to manage sensitive information, communicate with customers, process payments, and operate their businesses.

A single compromised email account, an outdated system, or an employee clicking a malicious link can expose sensitive information, interrupt business operations, and create significant financial and regulatory consequences.

The good news? Improving cybersecurity does not always require a large IT department or an expensive security infrastructure.

It begins with understanding your risks, establishing good security practices, and making cybersecurity an ongoing part of your daily operations.

Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

How Employee Cybersecurity Awareness Training Reduces Compliance Risks for Small Businesses

How Employee Cybersecurity Awareness Training Reduces Compliance Risks for Small Businesses

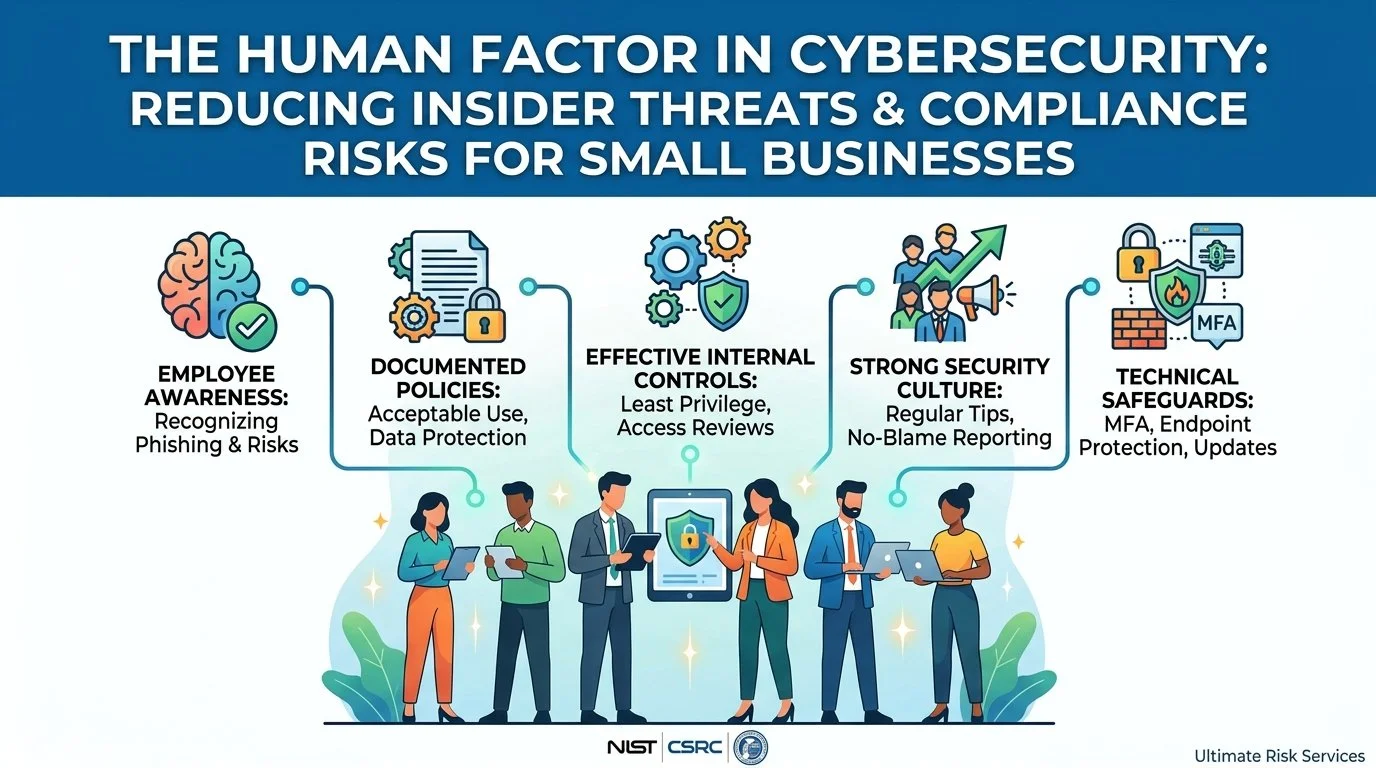
The Human Factor in Cybersecurity: How Small Businesses Can Reduce Insider Threats and Compliance Risks

Why employee awareness, documented policies, and effective internal controls are essential to protecting business data.

Cybersecurity incidents do not always begin with sophisticated hackers breaking through advanced security systems. Sometimes, they start with an employee clicking a fraudulent email link, sharing sensitive information with the wrong person, reusing a compromised password, or downloading unauthorized software.

For small businesses, these seemingly minor actions can lead to significant consequences, including data breaches, operational disruptions, financial losses, and regulatory compliance issues.

Employees are not necessarily the enemy. In many cases, they are the first line of defense against cyber threats. The challenge is ensuring they understand their responsibilities, recognize potential risks, and follow established security procedures.

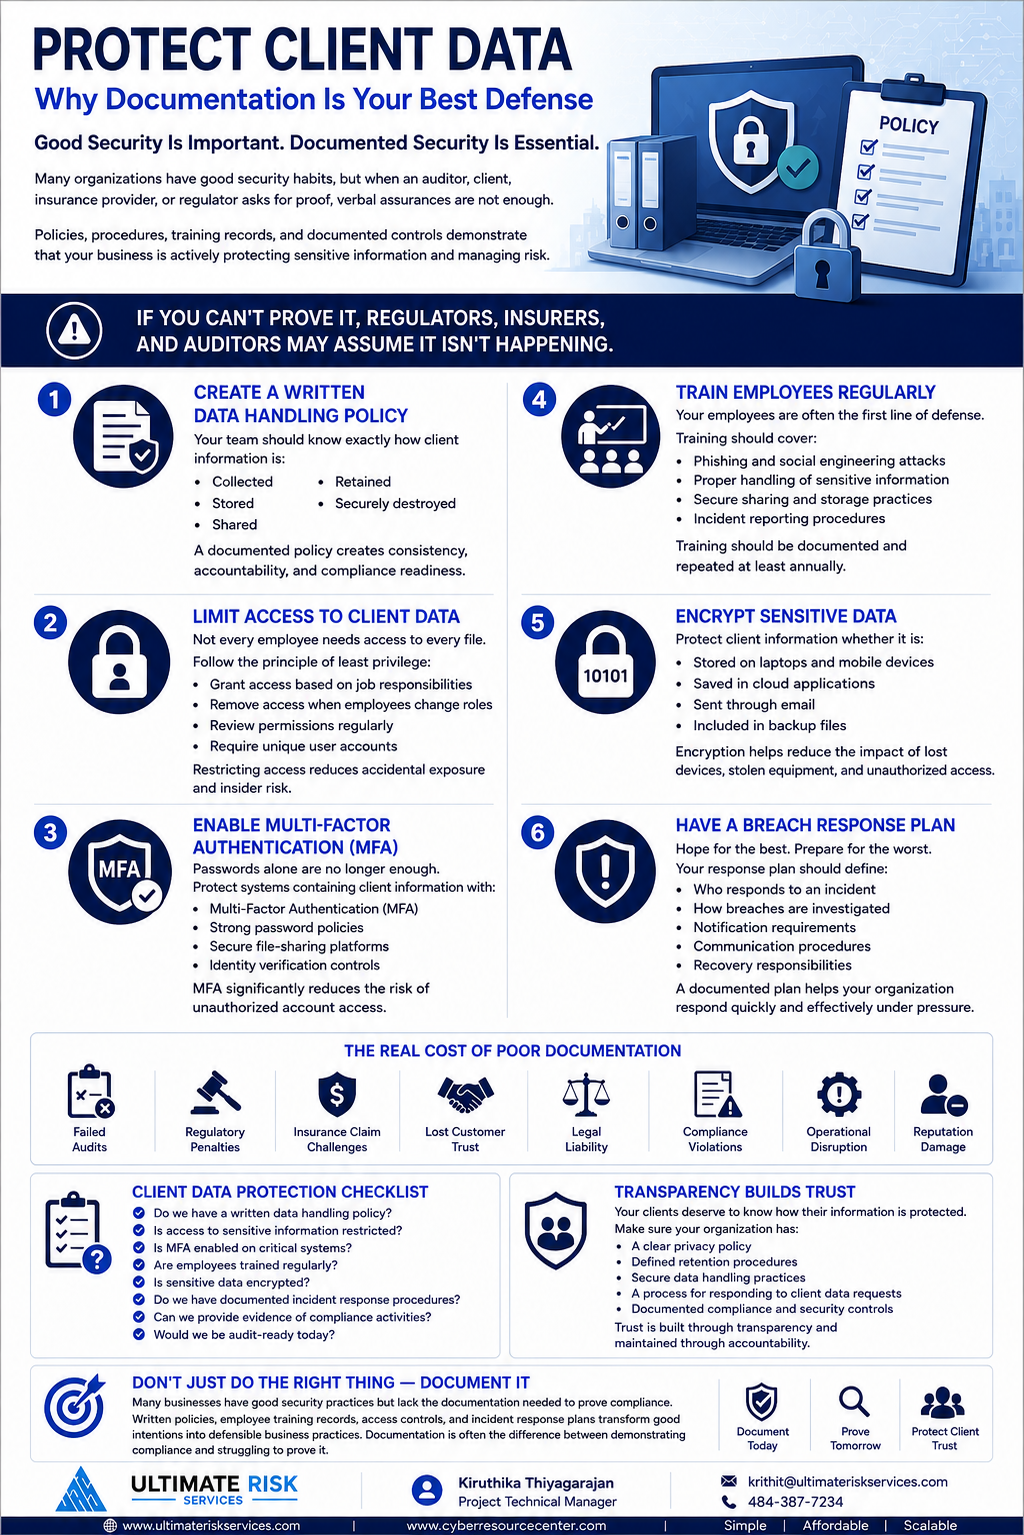
From a cybersecurity compliance perspective, protecting an organization requires more than installing antivirus software or deploying firewalls. It requires a documented, repeatable approach to managing human-related security risks.

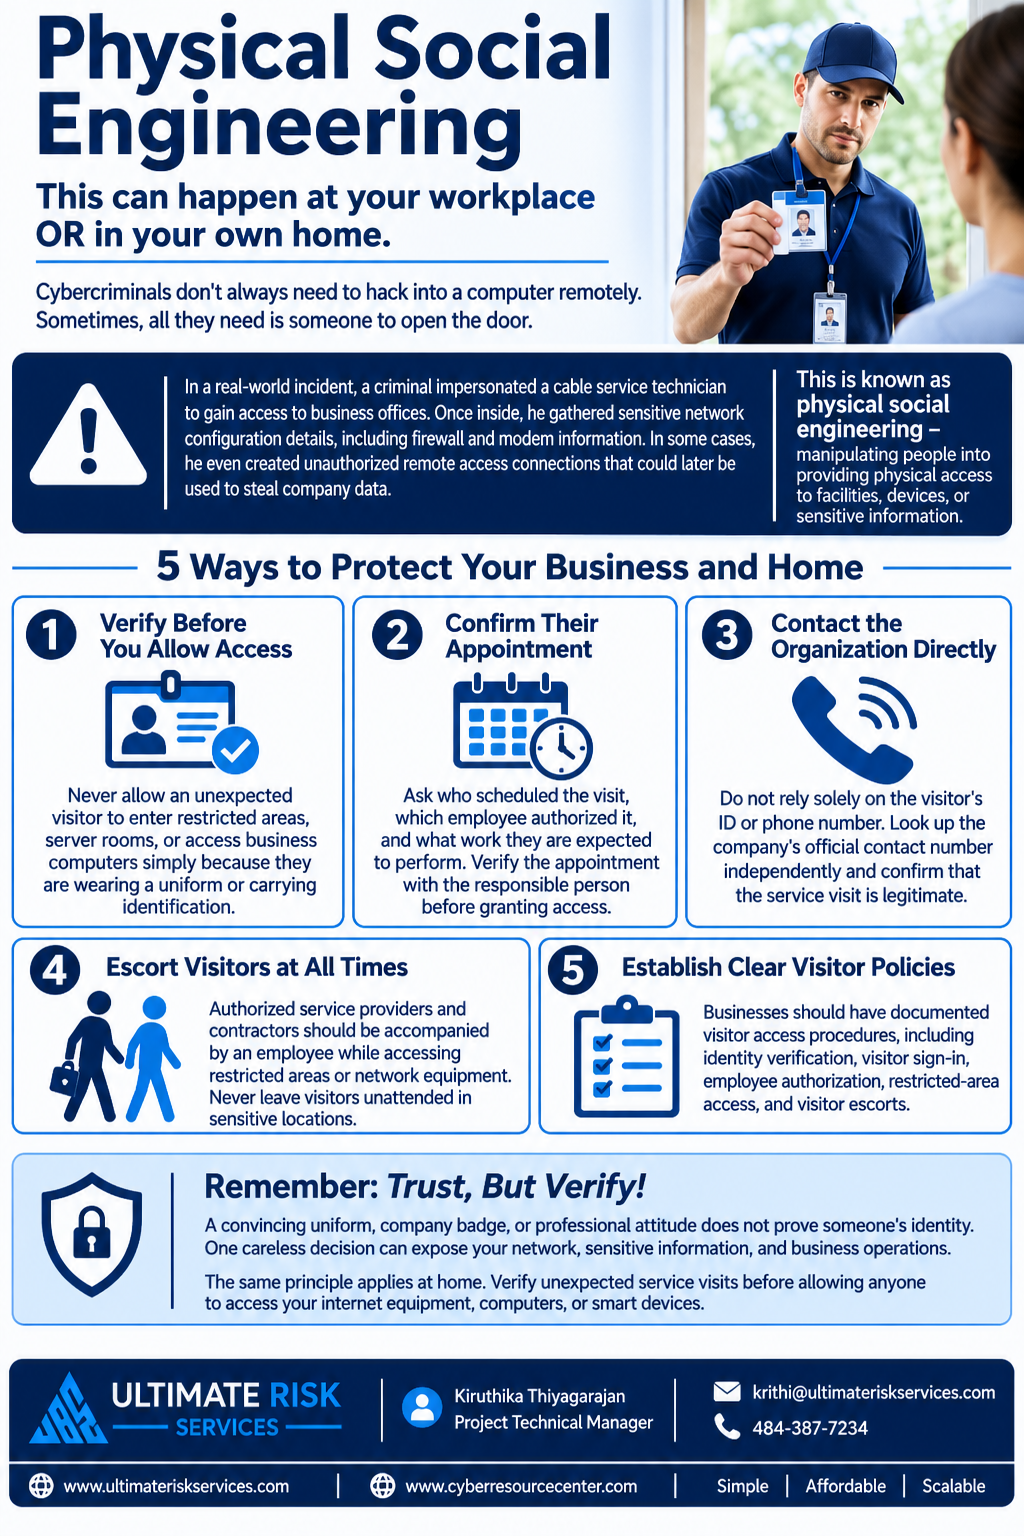
Why You Should Never Give Guests Access to Your Primary WiFi Network

Why You Should Never Give Guests Access to Your Primary WiFi Network

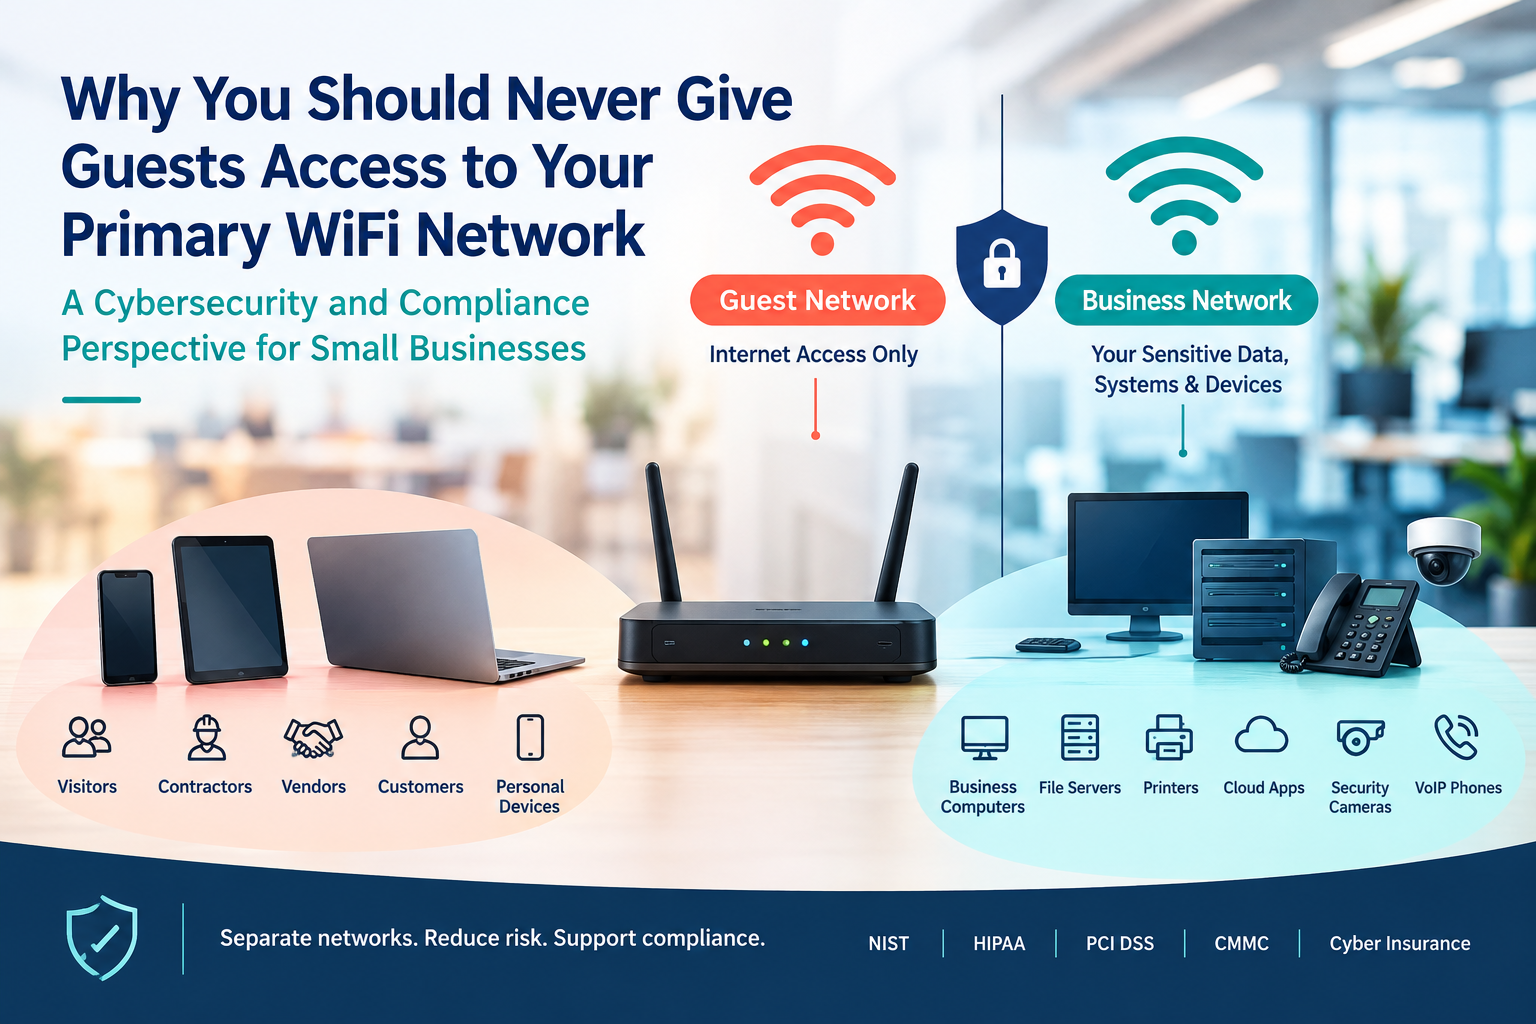
Many small businesses freely share their primary WiFi password with visitors, contractors, vendors, customers, and even employees' personal devices. It seems harmless. After all, they only need internet access for a short period of time.

Unfortunately, allowing guests onto your primary business network creates unnecessary cybersecurity, compliance, and operational risks.

From a compliance perspective, guest access is not simply an IT issueโ€”it is a risk management issue. Whether your organization follows NIST, HIPAA, PCI DSS, CMMC, or cybersecurity insurance requirements, network segmentation is considered a fundamental security control designed to reduce exposure to sensitive business systems and data.

Cybesecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

Apple Patched 273 Flaws in One Go: What SMBs and Executives Need to Know

Apple Patched 273 Flaws in One Go: What SMBs and Executives Need to Know

Many people assume Apple devices are automatically secure.

While Apple has a strong security reputation, no technology is immune to vulnerabilities. In fact, Apple recently released one of the largest security updates in its history, fixing 273 security vulnerabilities across iPhones, iPads, Macs, Apple Watches, Apple TVs, Vision Pro devices, Safari, and Xcode.

The update affects virtually every Apple platform and highlights an important reality:

Cybersecurity is not about which device you use. It's about how quickly you respond when security issues are discovered.

Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

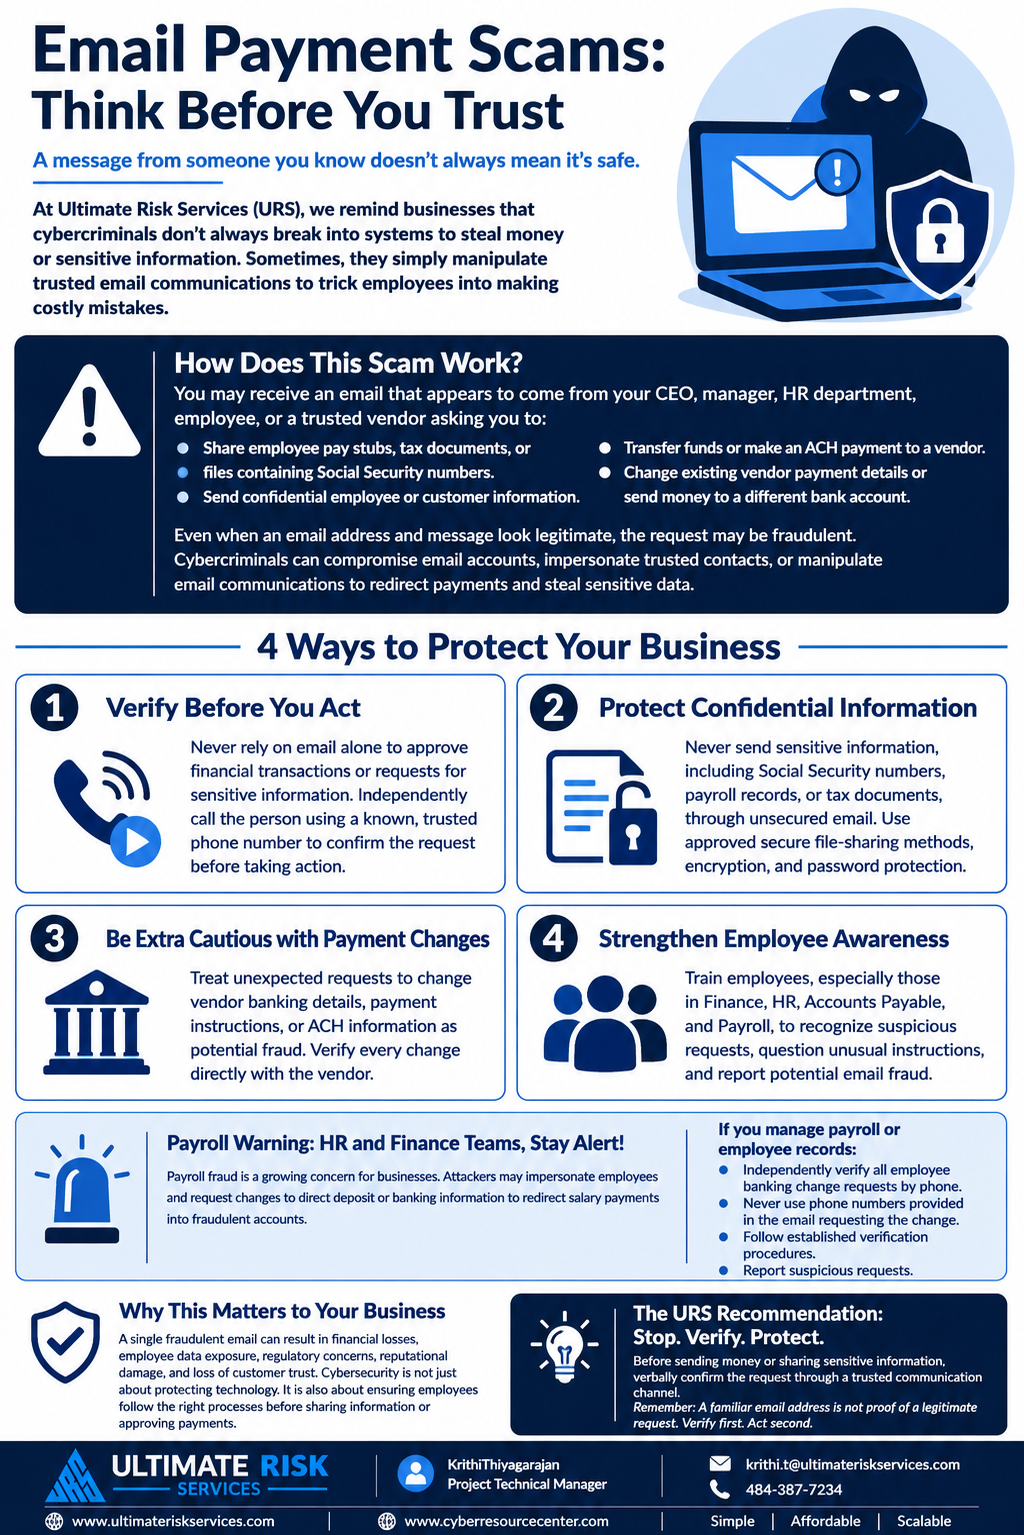
Identity Security Is Compliance Security: Addressing Today's Most Common Attack Methods

Identity Security Is Compliance Security: Addressing Today's Most Common Attack Methods

When MFA Isn't Enough: The Compliance Risks Behind QR Code Phishing and Modern Account Takeovers

For years, organizations have been told that enabling multi-factor authentication (MFA) is one of the most effective ways to protect user accounts.

And it is.

But today's attackers are no longer focused on breaking technology. They are focused on exploiting people.

Instead of guessing passwords or launching sophisticated technical attacks, cybercriminals are taking advantage of everyday actions employees perform without a second thoughtโ€”scanning a QR code, approving a login request, or granting access to a seemingly legitimate application.

As a result, organizations that believe they have strong authentication controls in place are still experiencing account compromises, business email fraud, data exposure incidents, and compliance failures.

This is no longer just a cybersecurity problem.

It is a compliance problem.

Because when an employee account is compromised, auditors, regulators, clients, insurers, and business partners are not interested in whether MFA was enabled. They want to know whether your organization had effective controls in place to prevent, detect, and respond to the threat.

Cybersecurity Tip!

Ready to see where your company defenses stand?

๐Ÿ‘‰ Request your customized cyber vulnerability report today and stay ahead of threats.
๐Ÿ‘‰ Gain insights into your unique cybersecurity vulnerabilities with a custom report.
๐Ÿ‘‰ Train your team to be your first line of defense

๐Ÿ“ž Schedule a call today or ๐Ÿ“ง contact us for a consultation.

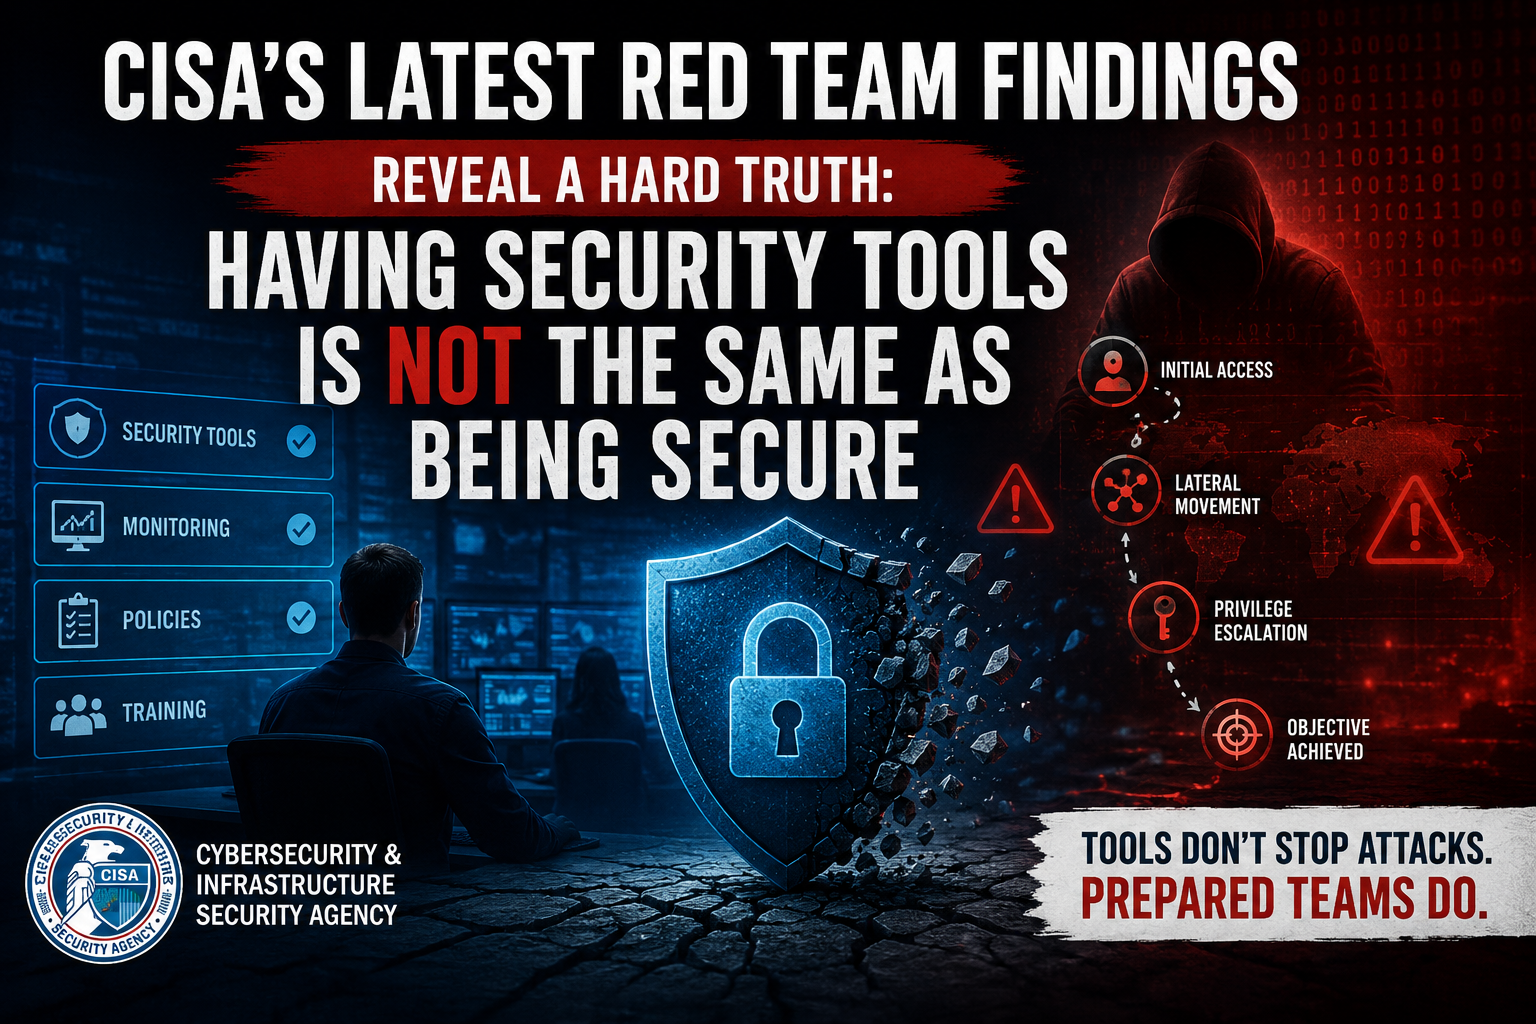
CISAโ€™s Latest Red Team Findings Reveal a Hard Truth: Having Security Tools Is Not the Same as Being Secure

CISAโ€™s Latest Red Team Findings Reveal a Hard Truth: Having Security Tools Is Not the Same as Being Secure

Many organizations invest heavily in cybersecurity tools. They deploy endpoint protection, collect logs, purchase security monitoring services, and implement security policies.

Yet when a real attacker gets in, many organizations still struggle to detect suspicious activity, investigate incidents, and respond before damage occurs.

A recent advisory from the U.S. Cybersecurity and Infrastructure Security Agency (CISA) highlights exactly why. Through authorized red team assessments conducted at two critical infrastructure organizations, CISA simulated real-world cyberattacks to evaluate how effectively organizations could detect, investigate, and respond to malicious activity. The results revealed significant gaps between having security controls in place and actually being prepared to stop an attack.